with an owner and a deadline.
A vulnerability is a security weakness, such as a bug in code. Exploiting it can put users, employees, data, and the company's reputation at risk, so someone needs to own the risk assessment and follow through on a resolution.Researchers report through your portal. Your team assigns an owner, replies, and tracks deadlines.
$8€6,9929,99 zł£5.99 per team member / month
Billed monthly. Security included in Kit. Plus tax.
First subscription: 30 days free. Card required.
See the reporting portal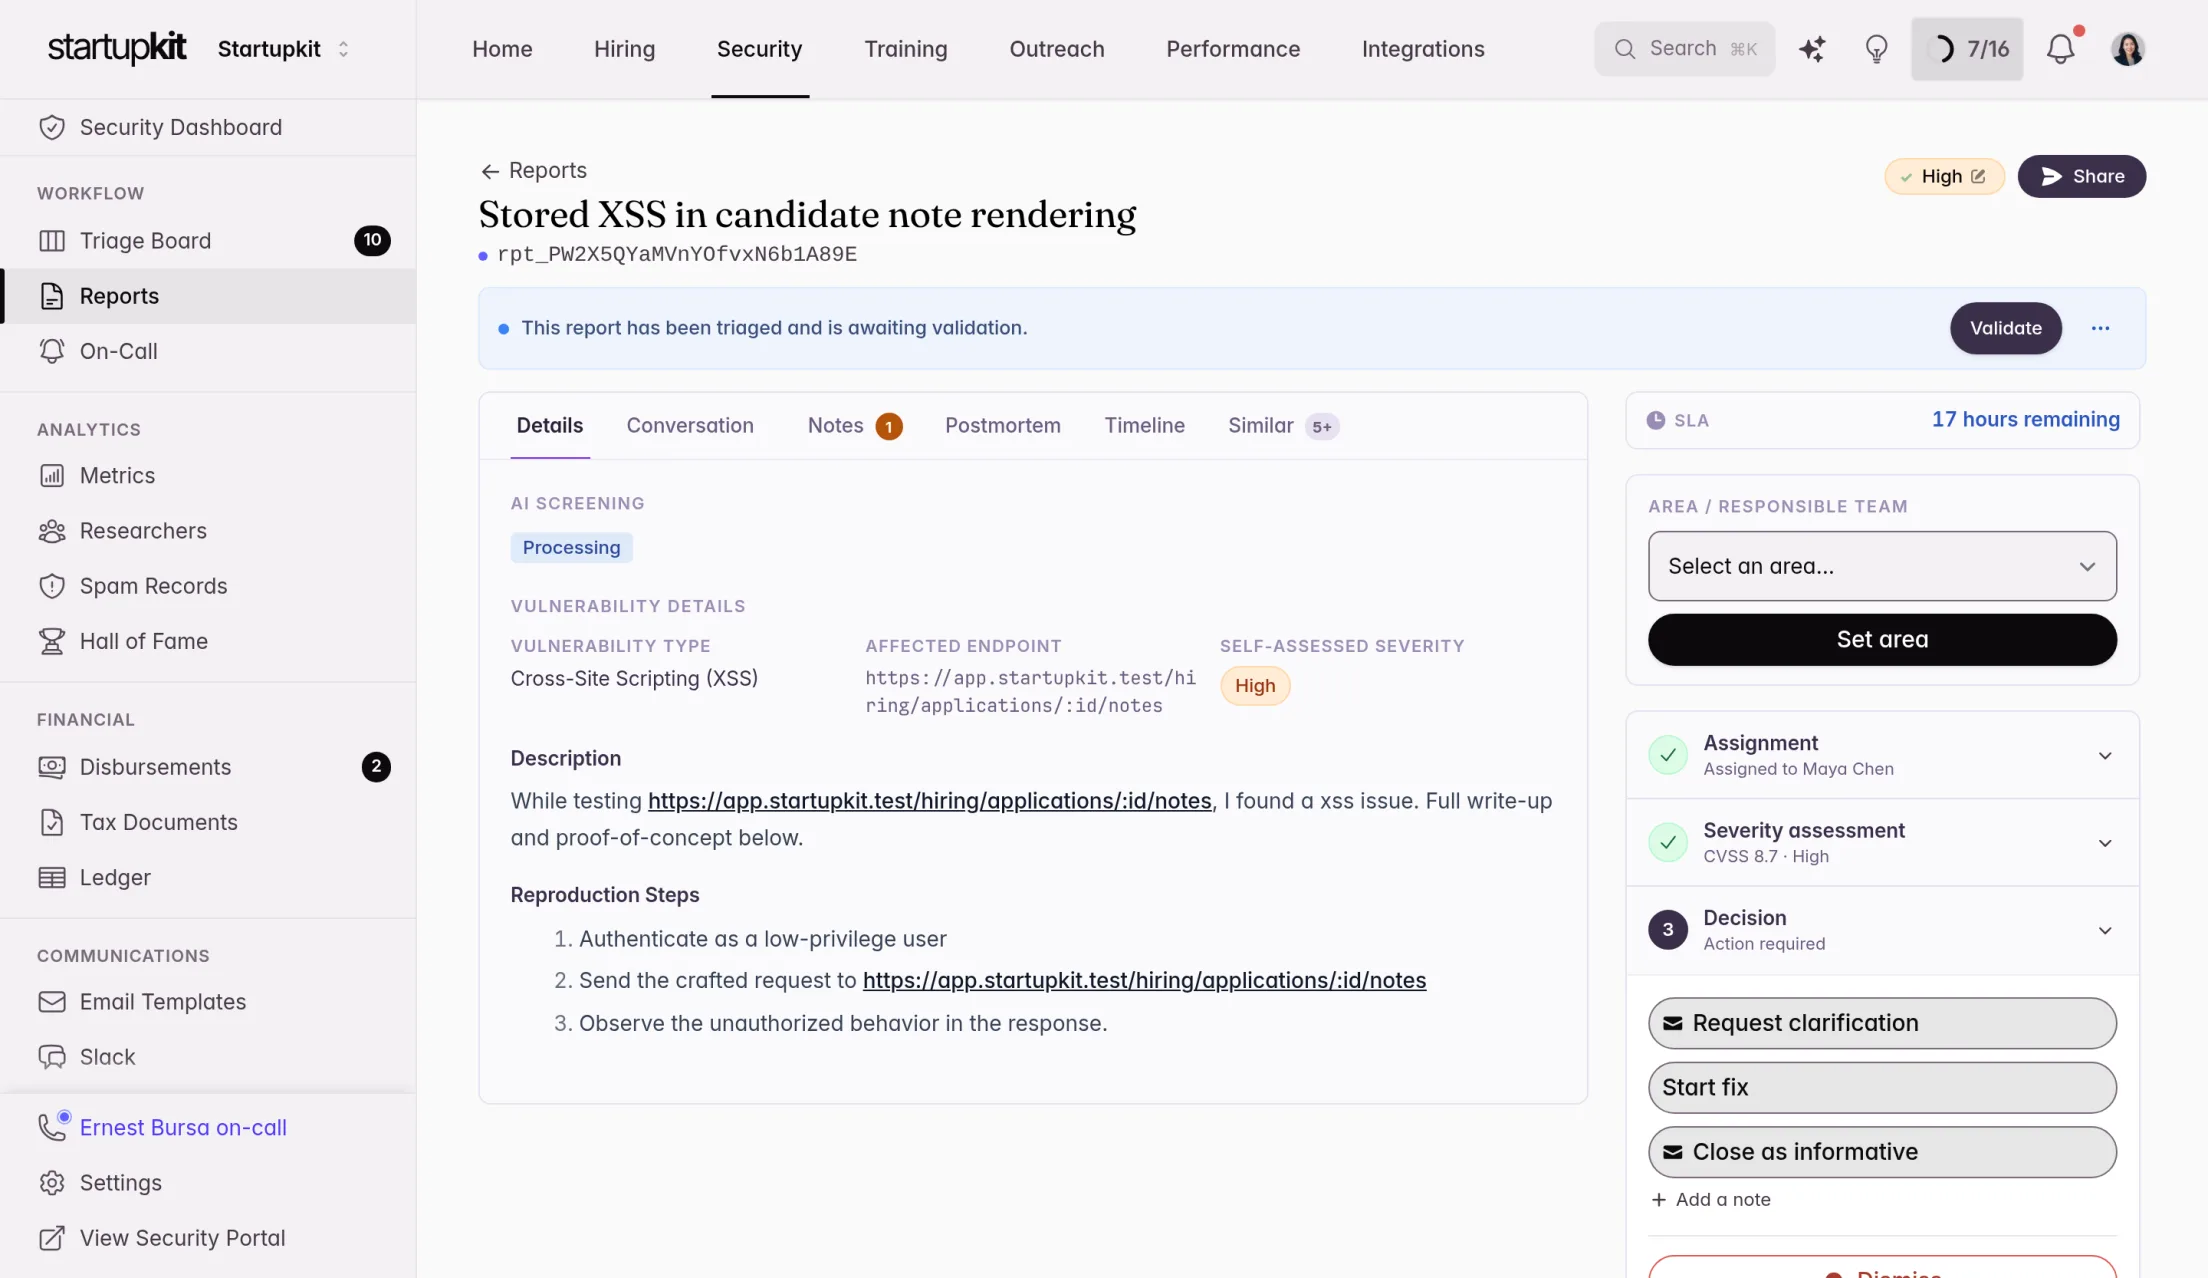
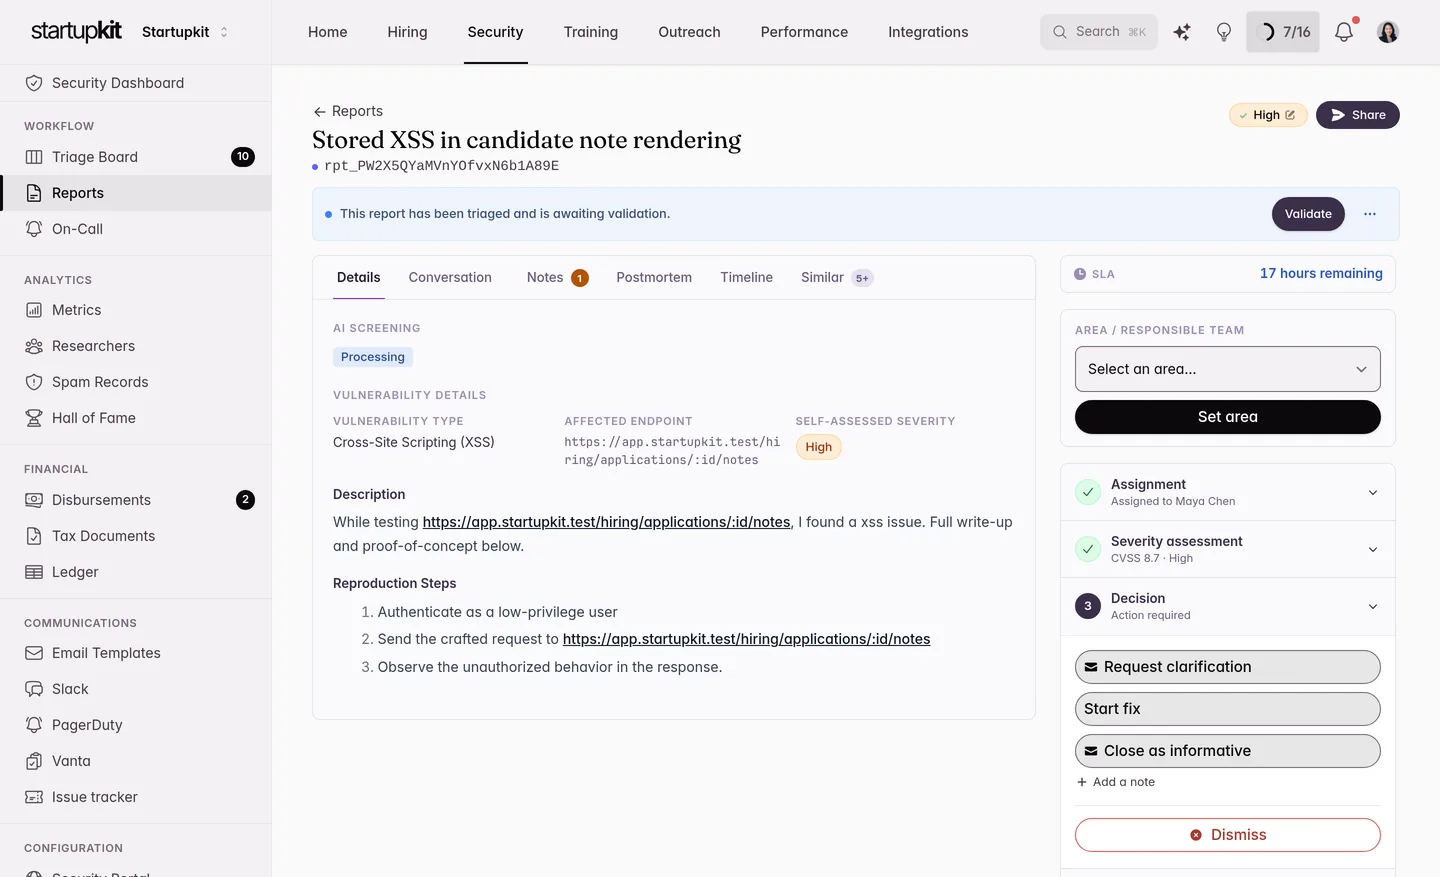
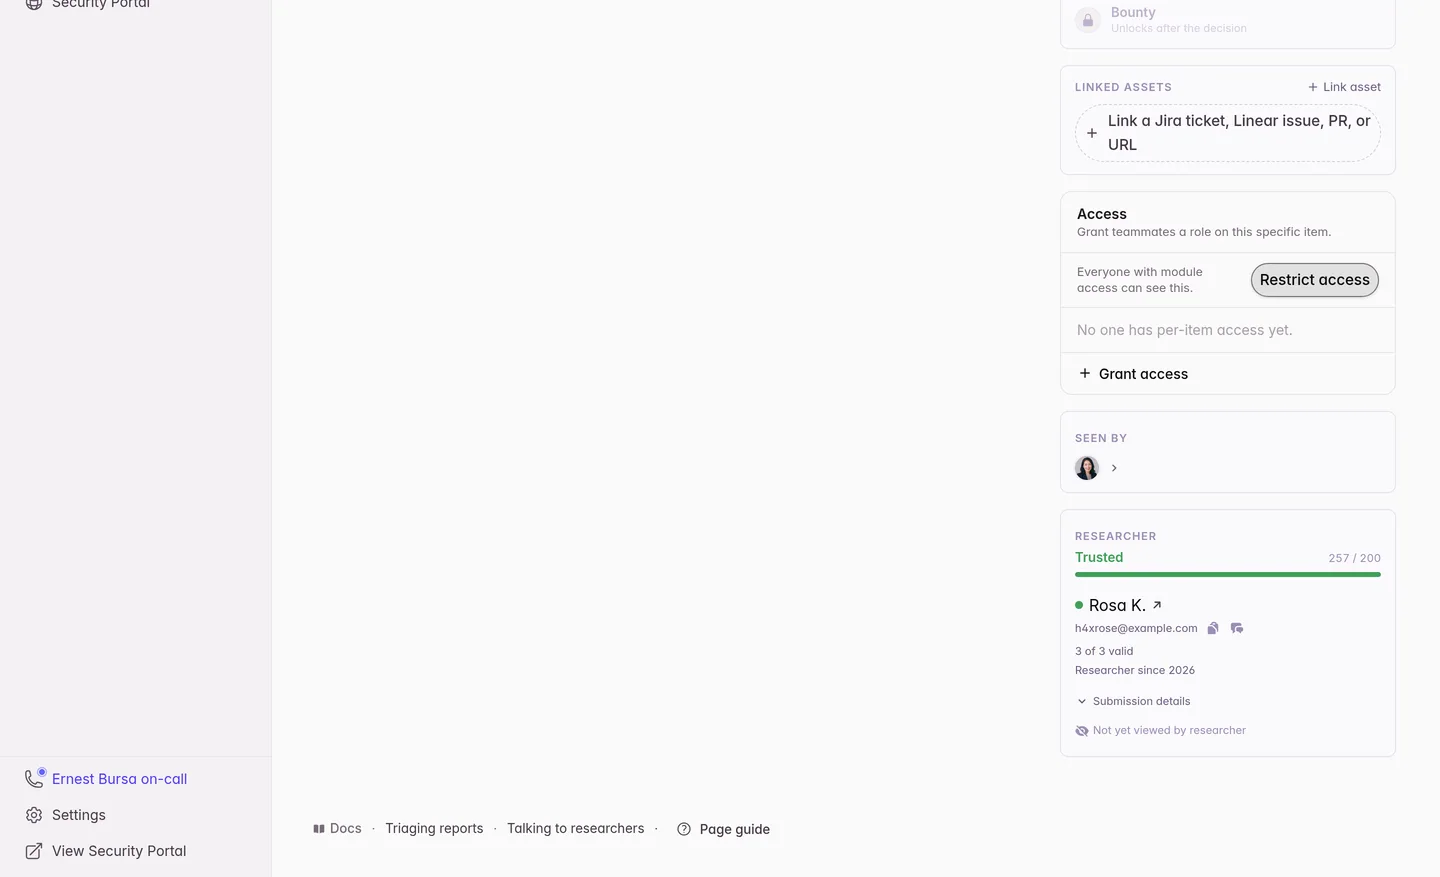
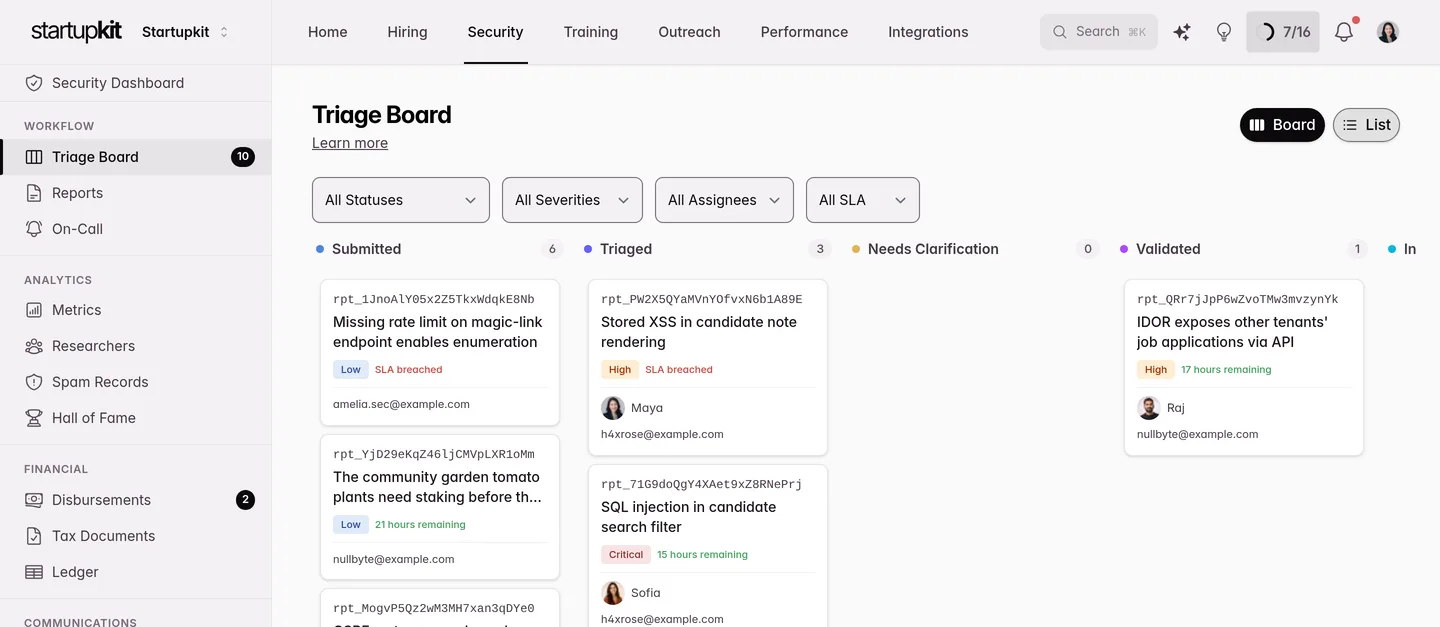
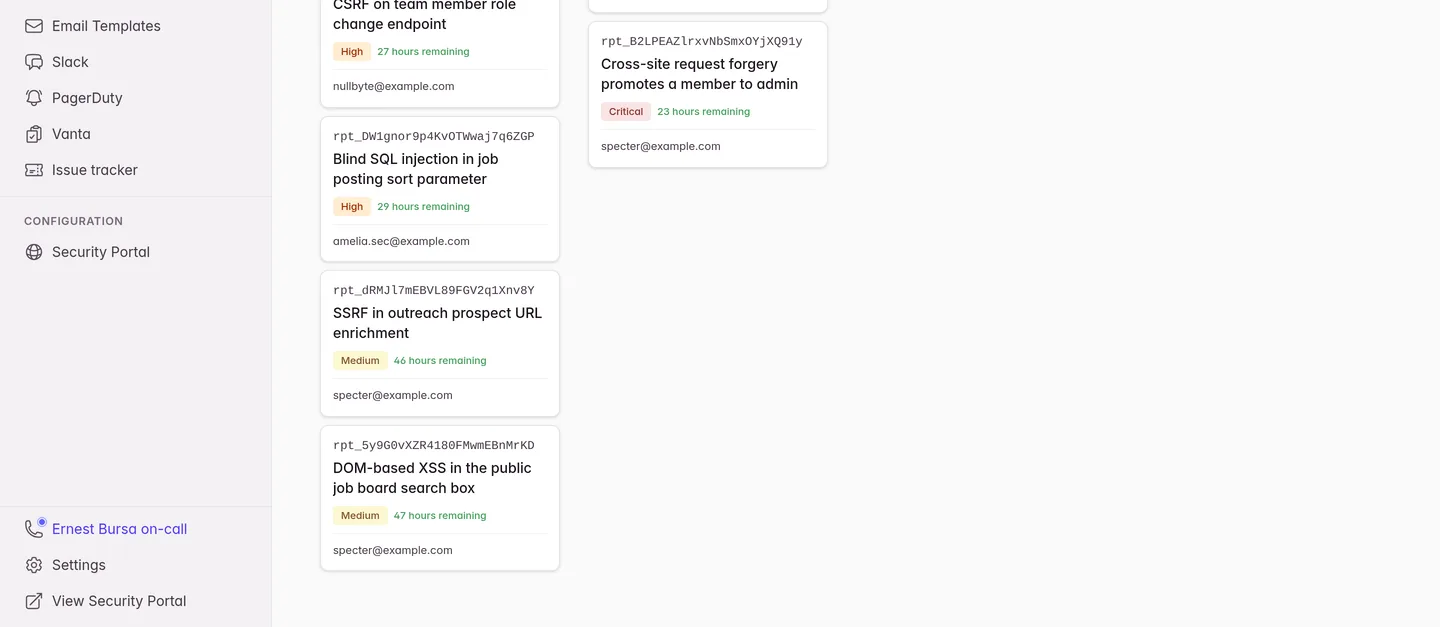
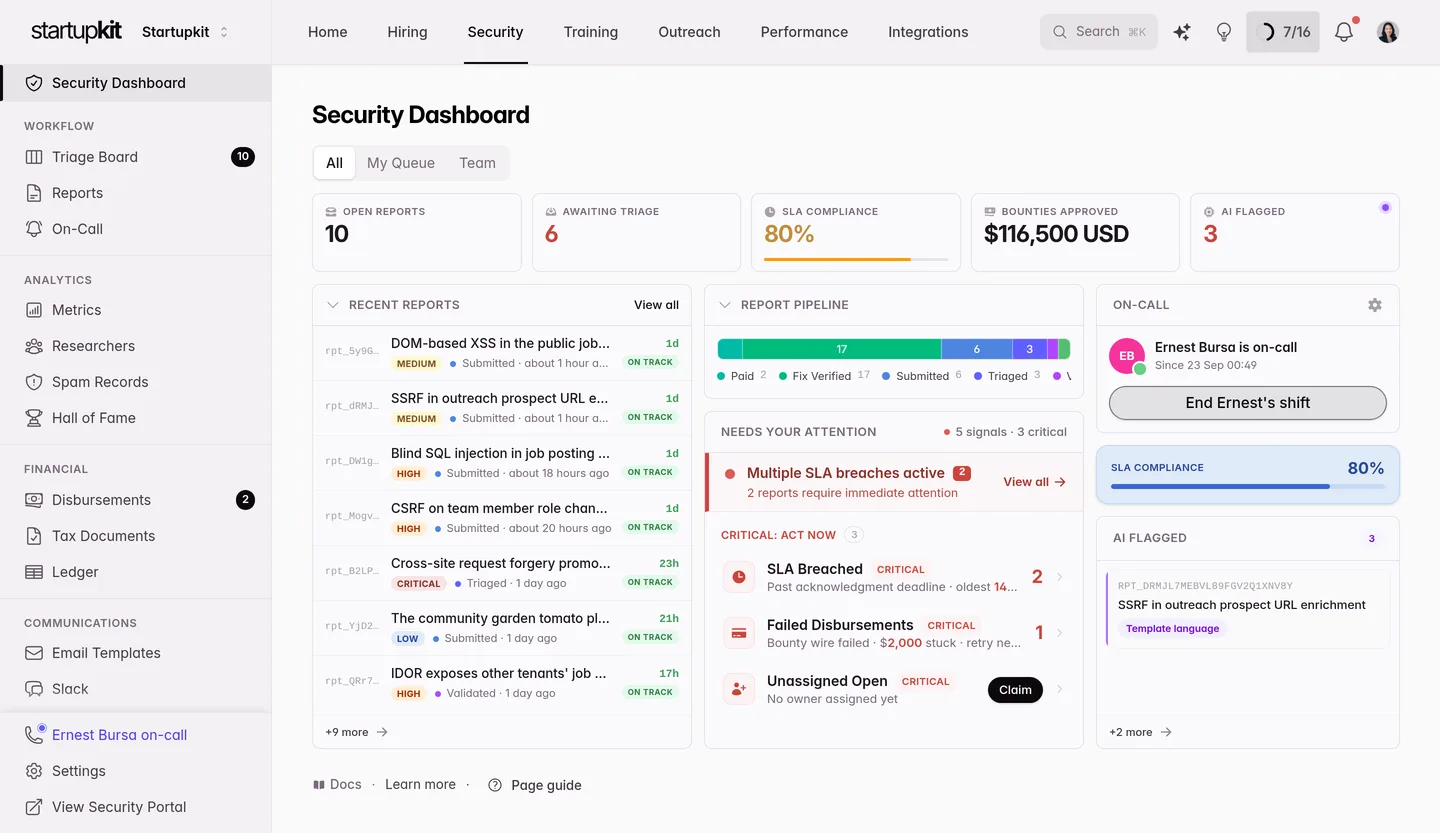
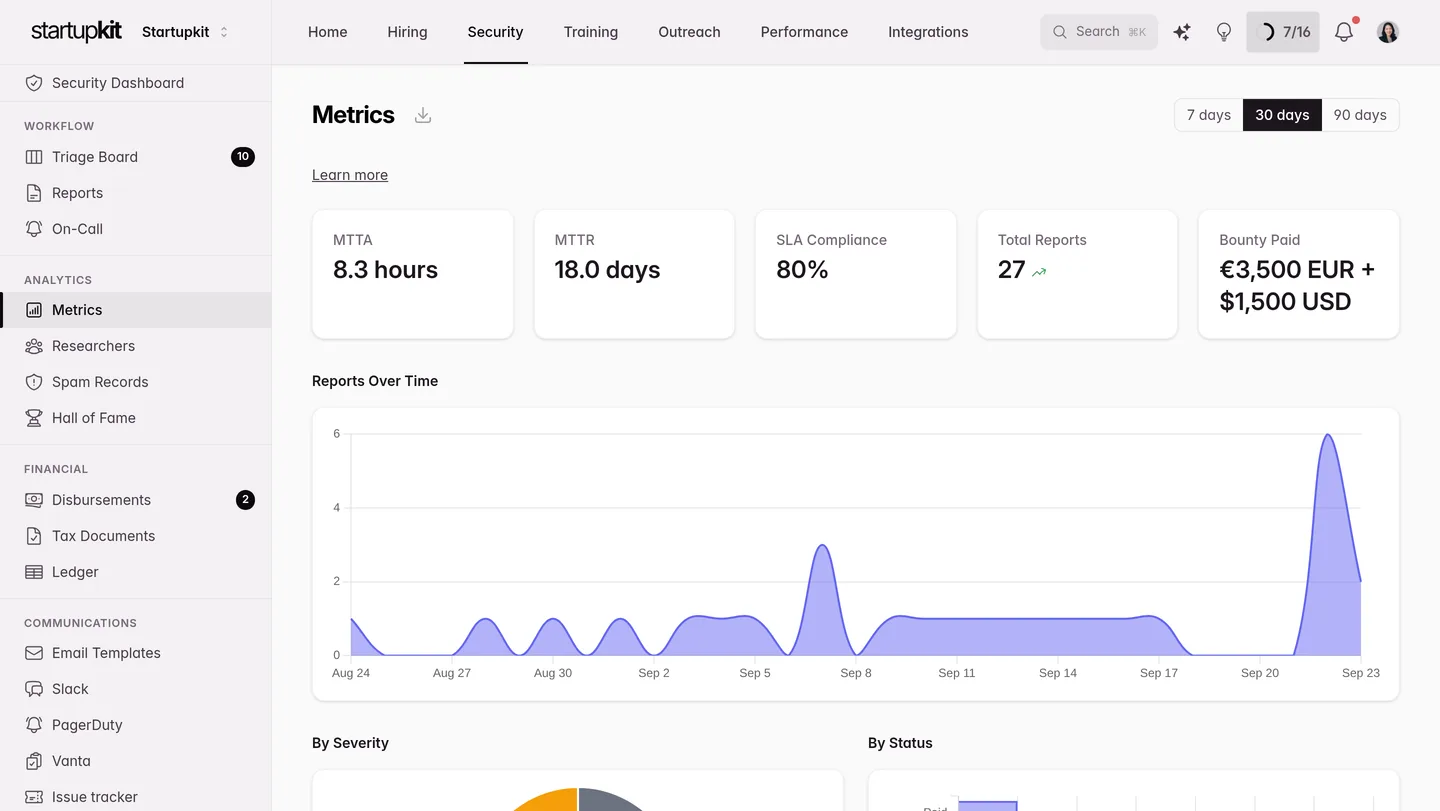
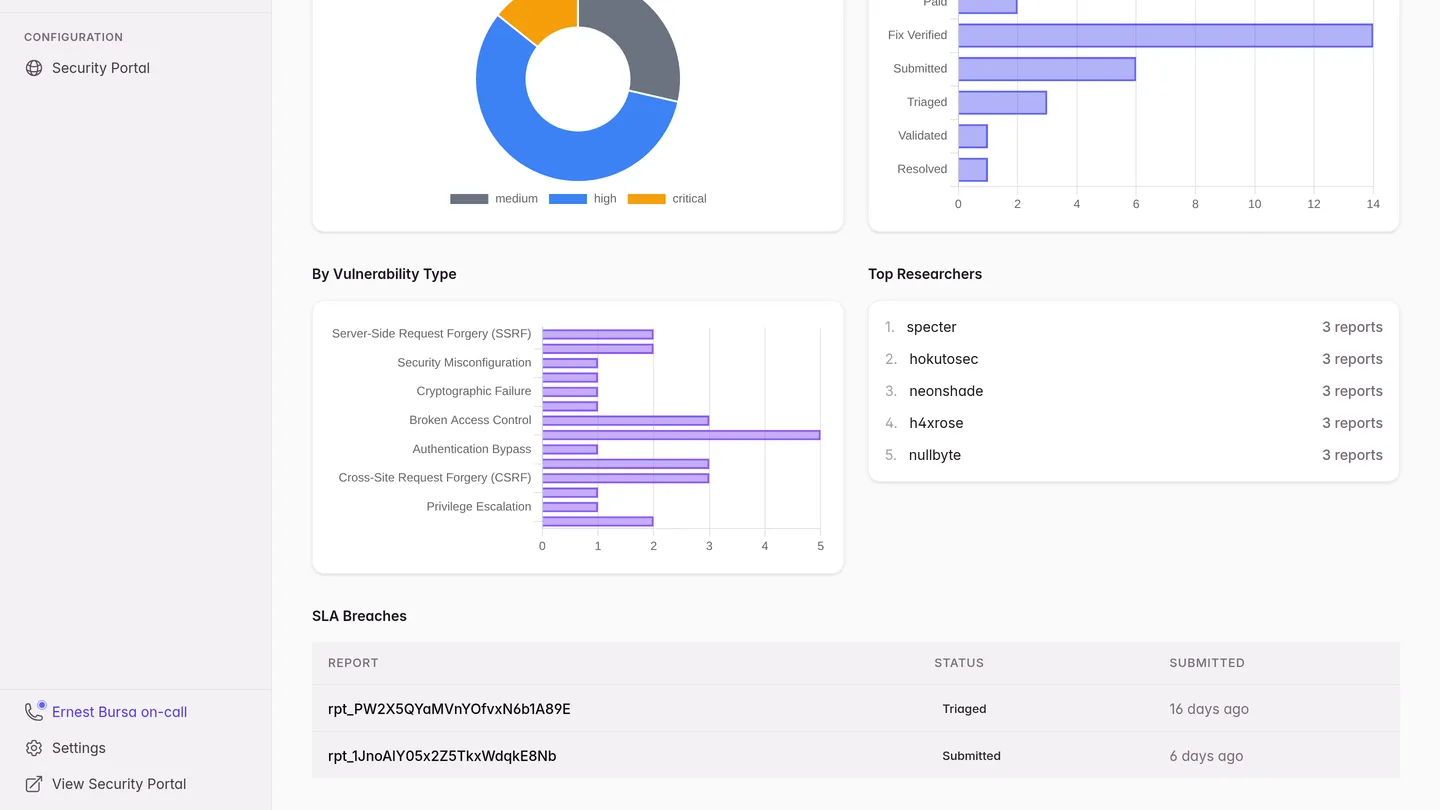
Give researchers a place to report and follow up.
Set your testing rules. Researchers send reproduction steps and attachments, then follow replies in their own portal.
Disclosure policy · security.txt · Custom domain
See the researcher portal guide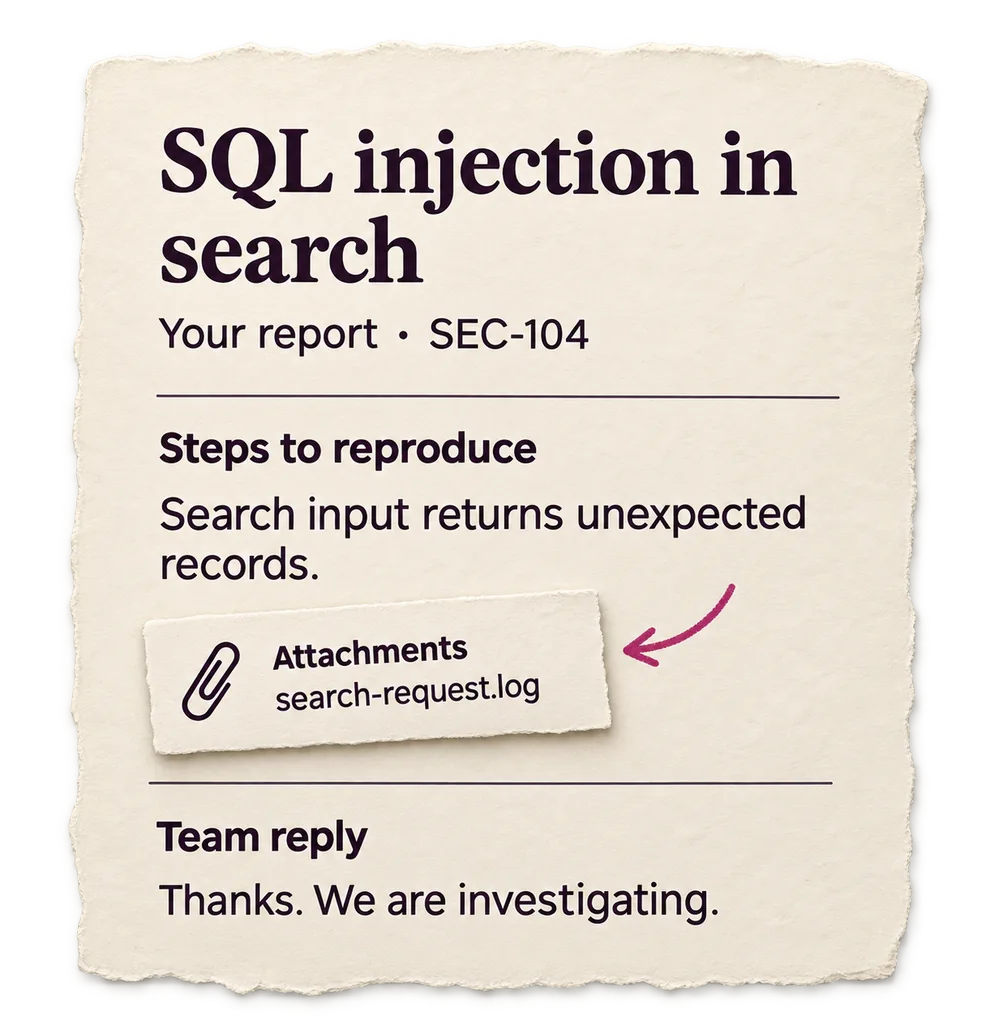
Run triage agents in your own CI.
Use your GitLab runner and model to investigate one report. Review reproduction notes, affected code and a suggested fix in the report.
Set up your triage agentYour AI assistant · MCP
Check duplicates, draft replies and use the tools your permissions allow.
Connect your assistant
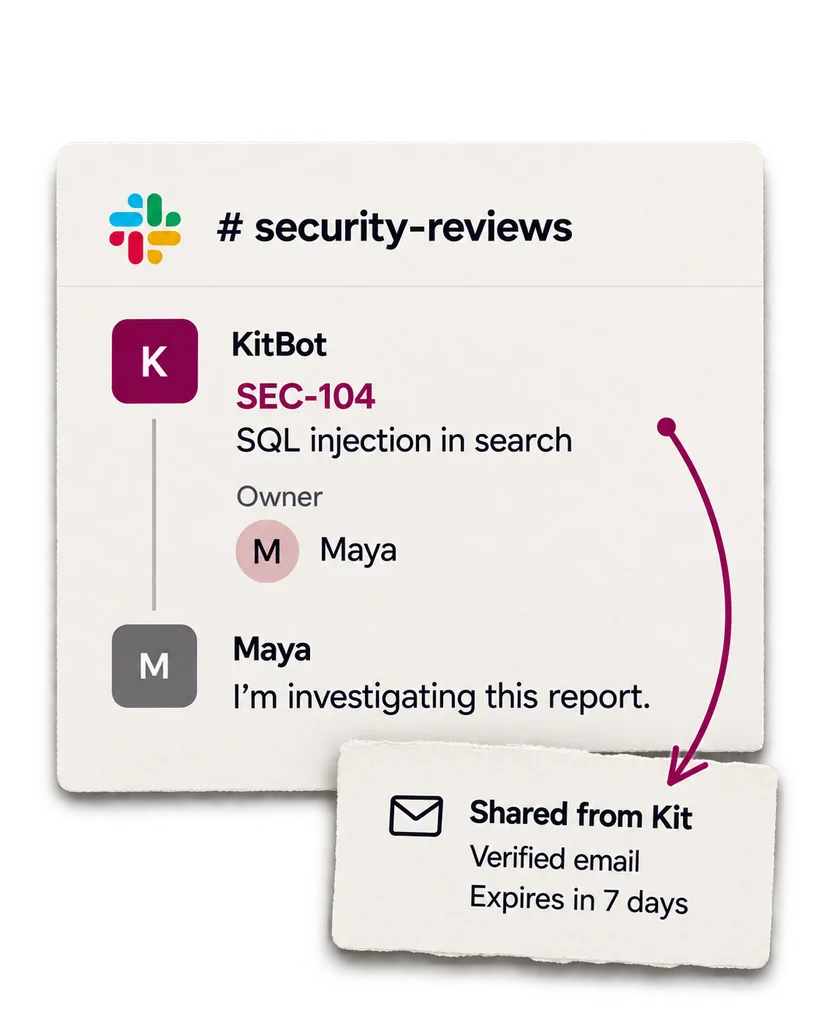
Follow reports in Slack. Bring in outside engineers.
Keep report updates in one Slack thread. Invite an outside engineer to a shared report with verified email access.
Link the fix. Export the incident record.
Create a Jira or Linear issue from the report. Export the timeline, assessment, postmortem and evidence manifest as an incident PDF.
Tracker issues omit full reproduction details by default.
Incident PDFs are generated in English.
See incident dossiers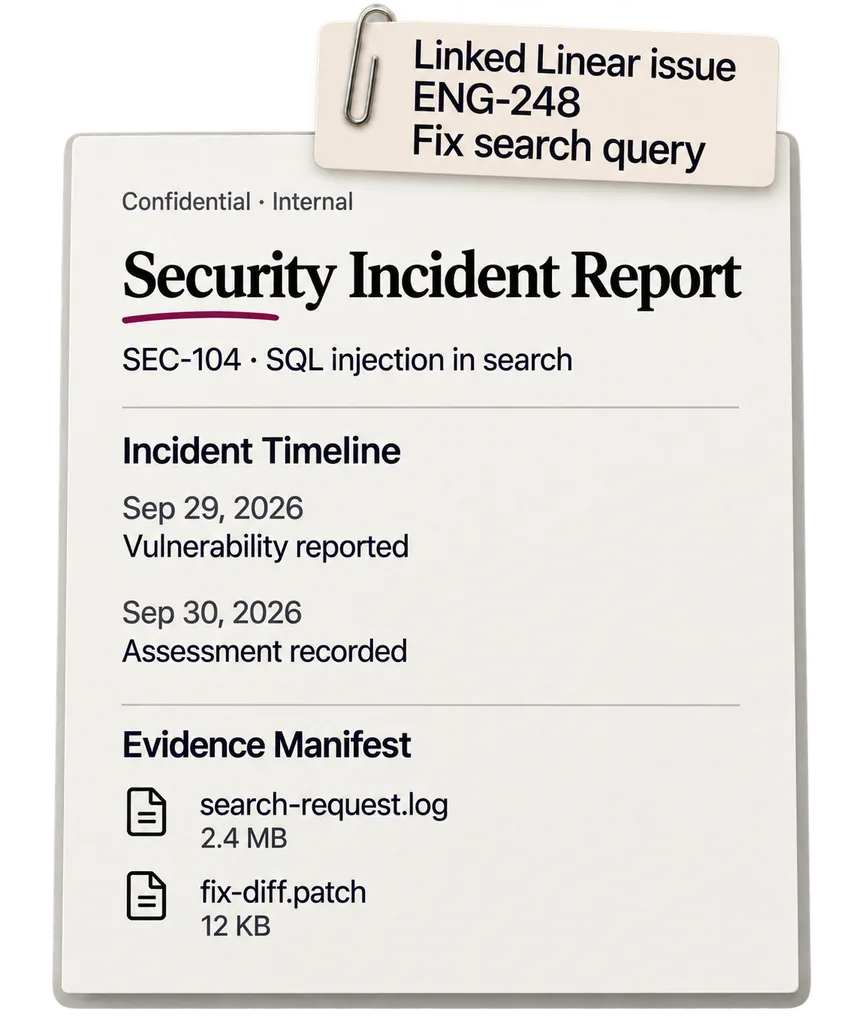
Security comes with your Kit subscription.
$8€6,9929,99 zł£5.99 per team member / month
Billed monthly. Security included in Kit. Plus tax.
First subscription: 30 days free. Card required.
Researcher access is free. Taxes extra.
Frequently asked questions
Who investigates and fixes vulnerabilities?
Your team. You manage intake, triage, replies and evidence. The subscription does not include researchers or responders.
Can we limit access by role and product?
Yes. Roles set starting permissions; you can adjust No access, Member or Admin for each product. Restrict sensitive reports to selected teammates; account and Security admins retain access.
Do we need to offer bounties?
No. Rewards are optional. Security admins approve bounty amounts. The Finance role provides payout and tax-document review without granting report access. Your team transfers the funds and records the payment.
Can we require an NDA and tax forms before payout?
Yes. Researchers provide payment details in their portal. You can require acceptance of your agreement, including an NDA, and a verified W-9 or W-8BEN before payout. Acceptance records include the agreement text, time and IP address.
Can we run a private program?
Yes. Invite researchers or approve requests for access.
How do you handle spam?
CAPTCHA and rate limits protect intake. AI screening uses your account’s AI allowance and flags reports for review. Report intake continues when that allowance is exhausted.
Can we take our data with us?
Yes. Export account data as JSON and incident dossiers as PDFs.
$8€6,9929,99 zł£5.99 /person/month /person/month
Get started free